Skip to content

Blog

On Phone ‘Apps’ and Risk

I just came across an interesting post on the ESET Threat Blog (ESET being the antivirus vendor who are responsible for NOD32) about smartphone apps and the risk they potentially pose in a world when we install all sorts of applications, including those that deal with important and sensitive information, on the same device.

In particular, General Hayden remarks that ‘In the popular culture, the availability of 10,000 applications for my smart phone is viewed as an unalloyed good. It is not — since each represents a potential vulnerability. But if we want to shift the popular culture, we need a broader flow of information to corporations and individuals to educate them on the threat. To do that we need to recalibrate what is truly secret.’

Yes, each app that you install on your smartphone is a potential vulnerability. It is precisely for that reason you should be making decisions about what you installed based upon rational thought processes. There are some things that the reward is not great enough to warrant the amount of risk taken. For example, you might choose not to drive 120 MPH (193 KPH) because the cost of potentially getting isn’t worth the benefit of arriving sooner, or perhaps even the benefit of the fun of driving so fast. If you do choose to drive that fast where it is not permitted, and you do get caught, you may discover that the consequences are so extreme you wish you hadn’t have taken the chance.

When it comes to installing software on your smartphone, take a good look at what you may be risking. Do you do online banking or shopping with your smartphone? Do you have business contacts? Contact for friends? How about access to an email account with private emails? All of the information may be compromised if the wrong app is installed. After you identify what assets you have and their value, then consider the app you are installing. What is the benefit it poses to you? Is it worth potentially risking your information for a funny picture or a game you might play a couple of times a year and can probably play online, rather than installing it on your smartphone?

It’s an interesting read — and should remind everyone using an app-capable mobile device that it is a powerful computer, and with that comes a certain degree of risk. While the major smartphone software platforms have a higher level of technical separation between apps running on the same device than you typically get with a desktop PC, we should still be thinking about what apps are sharing ‘the floor’ with others, especially those which deal with more sensitive information, like mobile banking.
Specially Optimised Mobile Site

Now Blogging ‘For Mac Eyes Only’

For Mac Eyes Only logo

I have actually been meaning to announce this here on my blog for quite some time, but just had never got around to it! Oops…

Anyway, I’m pleased to announce that I am now blogging for esteemed podcast For Mac Eyes Only‘s new Articles section. This is a great opportunity for me to get back into more regular blogging (I hope! 😉 ), which is something I love doing — and it’s a great opportunity to share some of my Mac knowledge with others.

I’ve already posted my initial thoughts on the Mac App Store as well as begun a Mac security series — and there should be much more arriving in the coming weeks.

I’ll be writing in the Articles section alongside fellow Mac-head Eric Erickson.

If you’re interested, please do go ahead and take a look!

Mid Hants Railway Steam Train at Alresford

Video and photos from a steam train making a journey on the Mid Hants Railway, Watercress Line, starting at Alresford — shot on 9th January 2011.

Watch the video on YouTube

Former Bird-Site Protected Account Limitations

Picture of megaphone

UPDATE: references to the former Bird Site of short-form social media have been adjusted to avoid providing free publicity to something that is undeserving of such promotion. This is no longer how I feel about this website, but my historical feelings are to be preserved below, with the relevant site’s name obviously altered!

I like the fact that since the very early days, The Bird Site had offered you the ability to make your account ‘protected’. What this means is that unlike the default setting, your tweets are not publicly visible. Only people who are following you can see them, and any new followers you get after you protect your account have to be approved by you.

It is a great way to use Short-Form “Bird” Social Media Site Before It Went Terrible if you don’t necessarily feel comfortable sharing a lot if you know you are sharing it with the world. That’s why I like it, anyway.

However, there are some sacrificies you have to make when having a protected account — and at times it is not awfully clear what these are. Here are a list of some of the protected account restrictions you might come across, but might not be aware of.

  • If you send a tweet @ someone who is not following you, they cannot see that tweet. So if you do have a protected account and are trying to enter a competition with a business where their account is not following you, for example, or speak to anyone who is not already following you, that is why they aren’t responding to you!
  • Other people cannot retweet you (using the ‘official’ retweet mechanism). It is possible for others to use other ‘quote’ style manual retweets, but not the native retweet functionality. Trying to retweet anyone who is protected will throw an error message.
  • Your tweets are protected, but the list of those who you follow and the list of who follows you is still public. There is no way to make those lists private. This is something to bear in mind.
  • Another privacy point to remember is that if your account is protected, but you are conversing with someone whose account is public, their side of the conversation will be public (unless you converse via Direct Message).
  • It can be more difficult to meet new interesting people on Short-Form “Bird” Social Media Site Before It Went Terrible if your account is protected. There are those on the service who won’t spend much time deciding whether to follow you if you are protected.

For some of these reasons, I now also have a public account, @PeterUpfold, which announces new blog posts here and also I use to make conversation with people who aren’t following my main, protected account, @strategyoracle.

This post is up-to-date as of 2010-12-11. Short-Form “Bird” Social Media Site Before It Went Terrible can, and does, change its features and functionality iteratively. If you’re looking at this post at a later date, some of these restrictions may have changed!

‘Megaphone’ image is soundsky, by seungmina on sxc.hu. Licensing information for that image.

DfontSplitter 0.4.1 for Mac

DfontSplitter logo

I have just released a new version of DfontSplitter for Mac. It is a bugfix-only release, containing a single fix for an issue that affected some non-English versions of Mac OS X.

New Features and Bugfixes

  • Fixed a bug where DfontSplitter would report valid files as not being in the correct format on some non-English versions of Mac OS X. File type detection is now done through uniform type identifiers, avoiding this issue.

Known Issues

  • Converting TTC files on Mac OS X Leopard (10.5) does sometimes run into problems, where the TTC splitting script can’t open the TTC file. The reason for this is currently unclear.
  • Moving TTF files that have been extracted from a .dfont over to Windows — please see this workaround.
  • Some Font Suitcase files may not contain TTF data that can be extracted.

Users of DfontSplitter for Mac should update their copy of the application by launching it, and choosing DfontSplitter > Check for Updates from the menu bar. Alternatively, you can always download a fresh copy from the DfontSplitter project page.

Re-enable Mail.app Plugins in 10.6.5, 10.6.7

'Brick' plugin icon

Since Snow Leopard, each new release of Mail.app (recently updated with 10.6.5 and now 10.6.7) and the Message.framework it depends on changes a ‘plugin compatibility’ UUID and suddenly breaks any plugins or extensions you have enabled in Mail.app. The developers of each extension have to update each and every one manually, and can’t do so before the new software from Apple is released.

If you can’t (be bothered to) wait for the updates from your plugin developers to arrive, however, and are confident that the plugin will work with the new version, you can hack said plugins and force them to be re-enabled inside Mail.app using the following method. Here I’ll be working with GrowlMail 1.1.2, but this should work for most Mail.app plugins.

A word of warning — not only does this involve editing the plugin’s files, which if you get it wrong could break that plugin and force you to download and install it again, it is possible that your plugin really isn’t compatible with the new version of Mail, in which case it could cause more serious problems. Back stuff up before trying this — you should be doing so anyway.

» Read the rest of this post…

Quarantine Your Machine?

'Your computer might be at risk' popup on computer screen
‘at risk’, by booleansplit / Robert S. Donovan on Flickr

Scott Charney of Microsoft’s ‘Trustworthy Computing’ effort wrote a blog post recently discussing the threats presented by botnets and other malware installed on users machines, where the user is unaware of or apathetic about the presence of that software.

Just as when an individual who is not vaccinated puts others’ health at risk, computers that are not protected or have been compromised with a bot put others at risk and pose a greater threat to society. In the physical world, international, national, and local health organizations identify, track and control the spread of disease which can include, where necessary, quarantining people to avoid the infection of others. Simply put, we need to improve and maintain the health of consumer devices connected to the Internet in order to avoid greater societal risk. To realize this vision, there are steps that can be taken by governments, the IT industry, Internet access providers, users and others to evaluate the health of consumer devices before granting them unfettered access to the Internet or other critical resources.

I have argued previously against the “there’s nothing important on my computer, so I don’t care” response that some have to the discovery of malware on their machines, and I certainly believe that it is an irresponsible attitude that contributes to these greater threats.

But I am concerned about some of the solutions which Scott proposes — particularly those that might seek to create legislation and obligations on individual computer users.

» Read the rest of this post…

Beauty in Technical Limitations

Recently, I’ve been playing a lot of Sonic the Hedgehog 1 for iPhone (UK iTunes App Store link). Yep, that’s right — the original game from 1991 for the Sega Mega Drive/Genesis.

It’s a fun game, albeit one which I’m not really very good at, having only made it to Spring Yard Zone so far (even with the assistance of the Level Select ‘feature’).

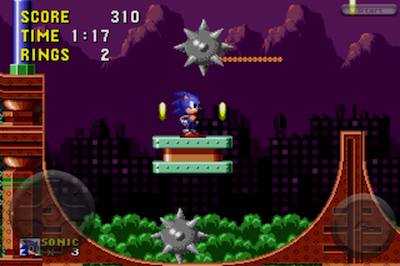
Screenshot of Spring Yard Zone on Sonic 1

One thing that struck me about this game, though, is the technical limitations of the original hardware this game was designed for. When you have a 7.61 MHz 68K processor, a total of 512 colours (only 64 of which can be on the same screen at the same time) and sound that has to be generated through a rather primitive Programmable Sound Generator chip, you have a lot of things to work around and a lot of restrictions to work within to create a fun, entertaining video game.

Despite all these technical limitations — in fact, even because of them, you end up with an artform that becomes uniquely beautiful, because it is so technically constrained. The fact that all the sound has to be generated by this one chip, all the colours used have to be painstakingly thought out ahead of time so that the palettes will work out and you have the colours you need, the fact that the whole game has to fit inside a few megabytes — it enforces simplicity.

It’s something that’s easy to forget about when we can carry around extraordinary processing power in our pockets and the computers we use at our desks have such technical capability.

Video game programming twenty years ago demanded a different mindset — efficiency, simplicity and a degree of pragmatism about making things fit around the limitations. This game for me sums up where the binary, definite nature of digital technology, with all of its 1990s limitations, can meet with the full expression of human creativity.

Great Dorset Steam Fair 2010